What this tutorial covers
Run a data-driven analysis for Zero-Trust / physical-security traces.
Before you start:You need access to the product and should ideally follow the tutorial using your own real parameters or data. The screenshots below were manually rematched to avoid the image/topic mismatches seen in the previous version.
Step-by-step workflow
1Open the module
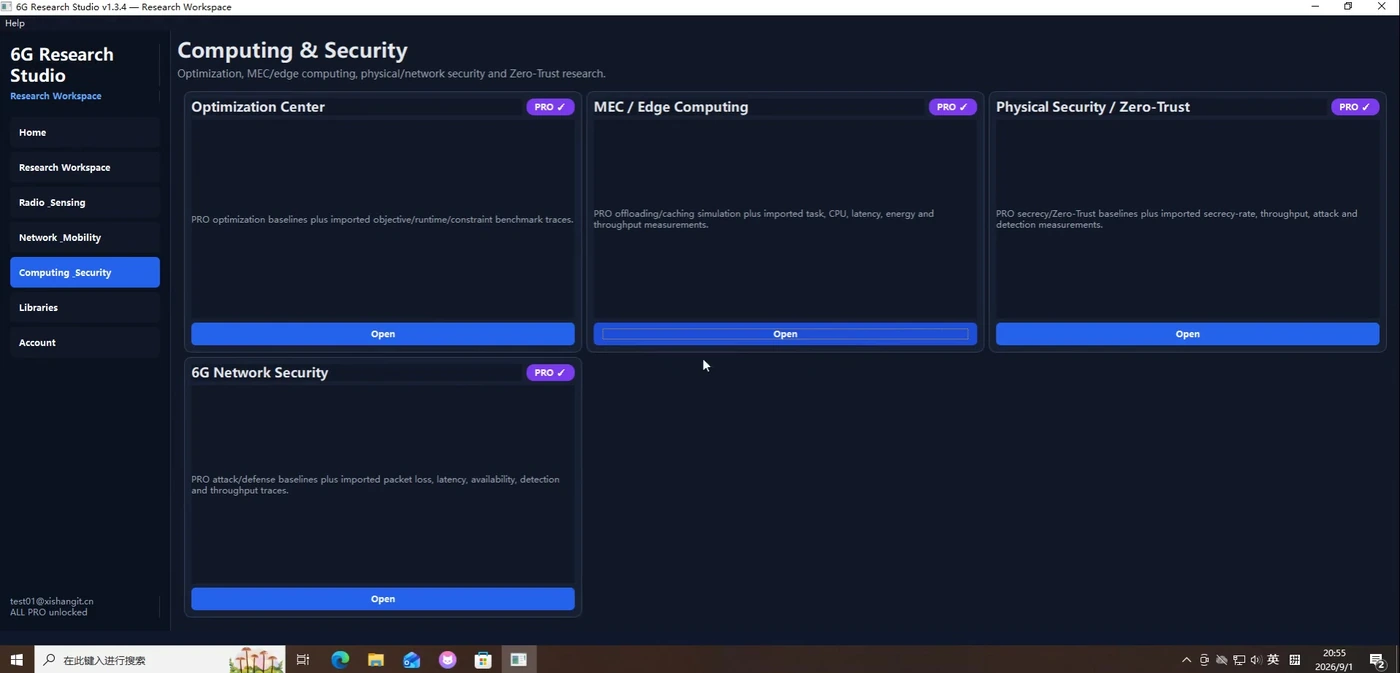
Open Physical Security / Zero-Trust from Computing & Security. Confirm that the visible page really matches the tutorial topic before changing any settings.
2Configure the input
Prepare and check security-trace data, metric choices and threshold settings.
3Run and watch the status
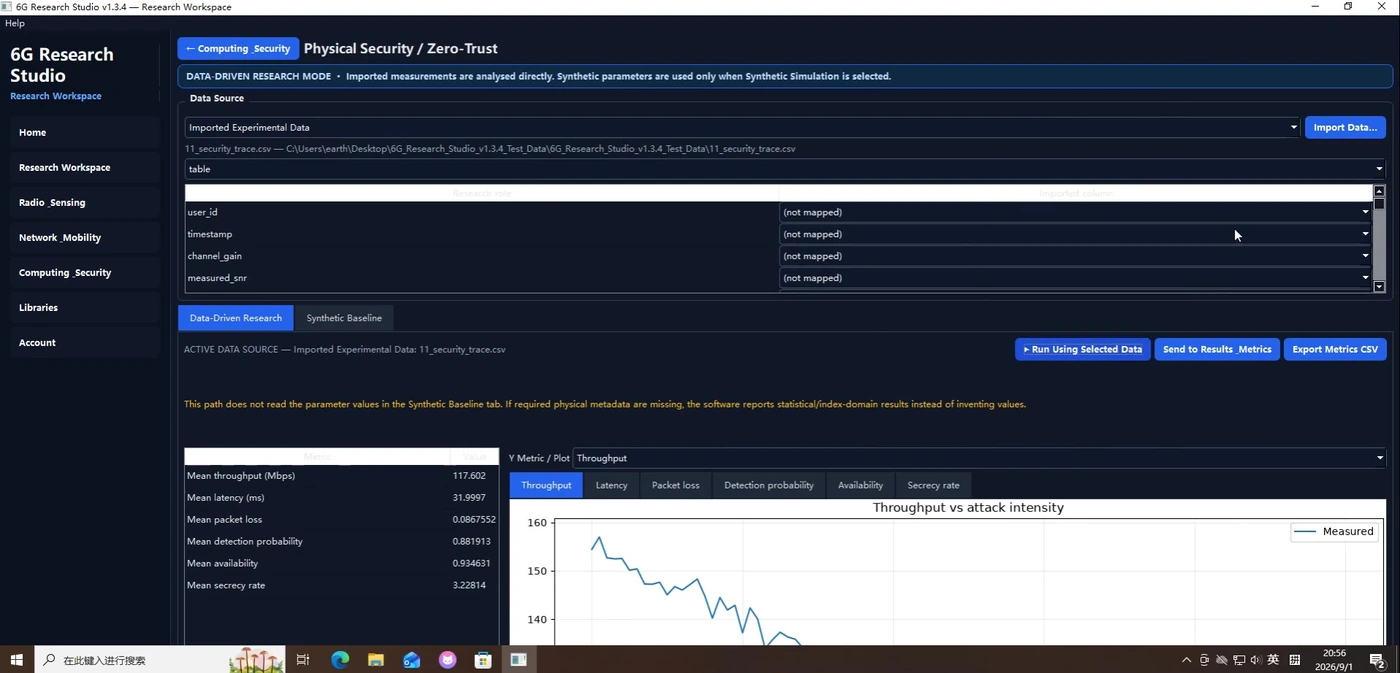
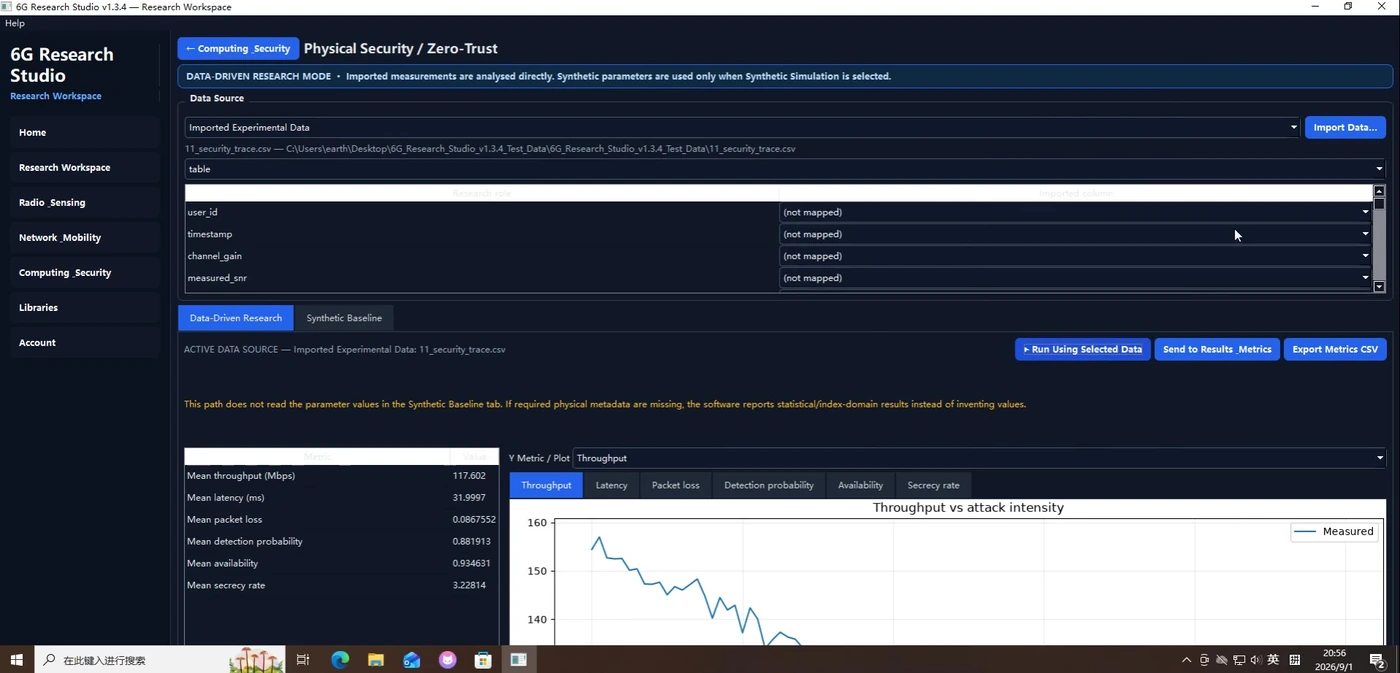
Import the data and switch across different metric views for analysis. Watch the visible status, plot or log area while the workflow is running.
4Inspect the result
Pay special attention to throughput, latency, packet-loss or other security-related plots.
5Verify and iterate
Interpret security results against the exact metric and scenario you are studying. Change one meaningful parameter and rerun so you can verify whether the output changes in the expected direction.
How to read the result
- The main output of this workflow is throughput, latency, packet-loss or other security-related plots.
- Read the result together with the exact inputs used for the run; a screenshot alone rarely tells the whole story.
- Interpret security results against the exact metric and scenario you are studying.
Troubleshooting & practical tips
- If nothing changes, first confirm that the correct module is open.
- If the output looks unrealistic, check units, field mapping and input scale first.
- For comparisons, change one key parameter at a time whenever possible.